
Network Segmentation Implementation Guide: Reducing Cyber Risk and Limiting Business Disruption
A ransomware event rarely stays confined to the first device it reaches. Once an attacker obtains credentials or compromises an endpoint, an unrestricted network can let them move from a workstation to file shares, servers, backups, cloud-connected systems, and customer data. A network segmentation implementation guide gives business leaders a practical way to limit that path and reduce the scale, cost, and insurability impact of an incident.
Segmentation is not simply an IT architecture project. It is a business protection control that helps contain operational disruption, protect regulated information, and demonstrate that access to critical systems is intentionally restricted. Done poorly, it can interrupt legitimate workflows. Done well, it makes the organization harder to compromise and easier to recover.
Network segmentation is one of the most effective controls for limiting ransomware spread. Even when attackers gain initial access, properly separated environments can prevent a local compromise from becoming a company-wide outage.
What Network Segmentation Actually Does
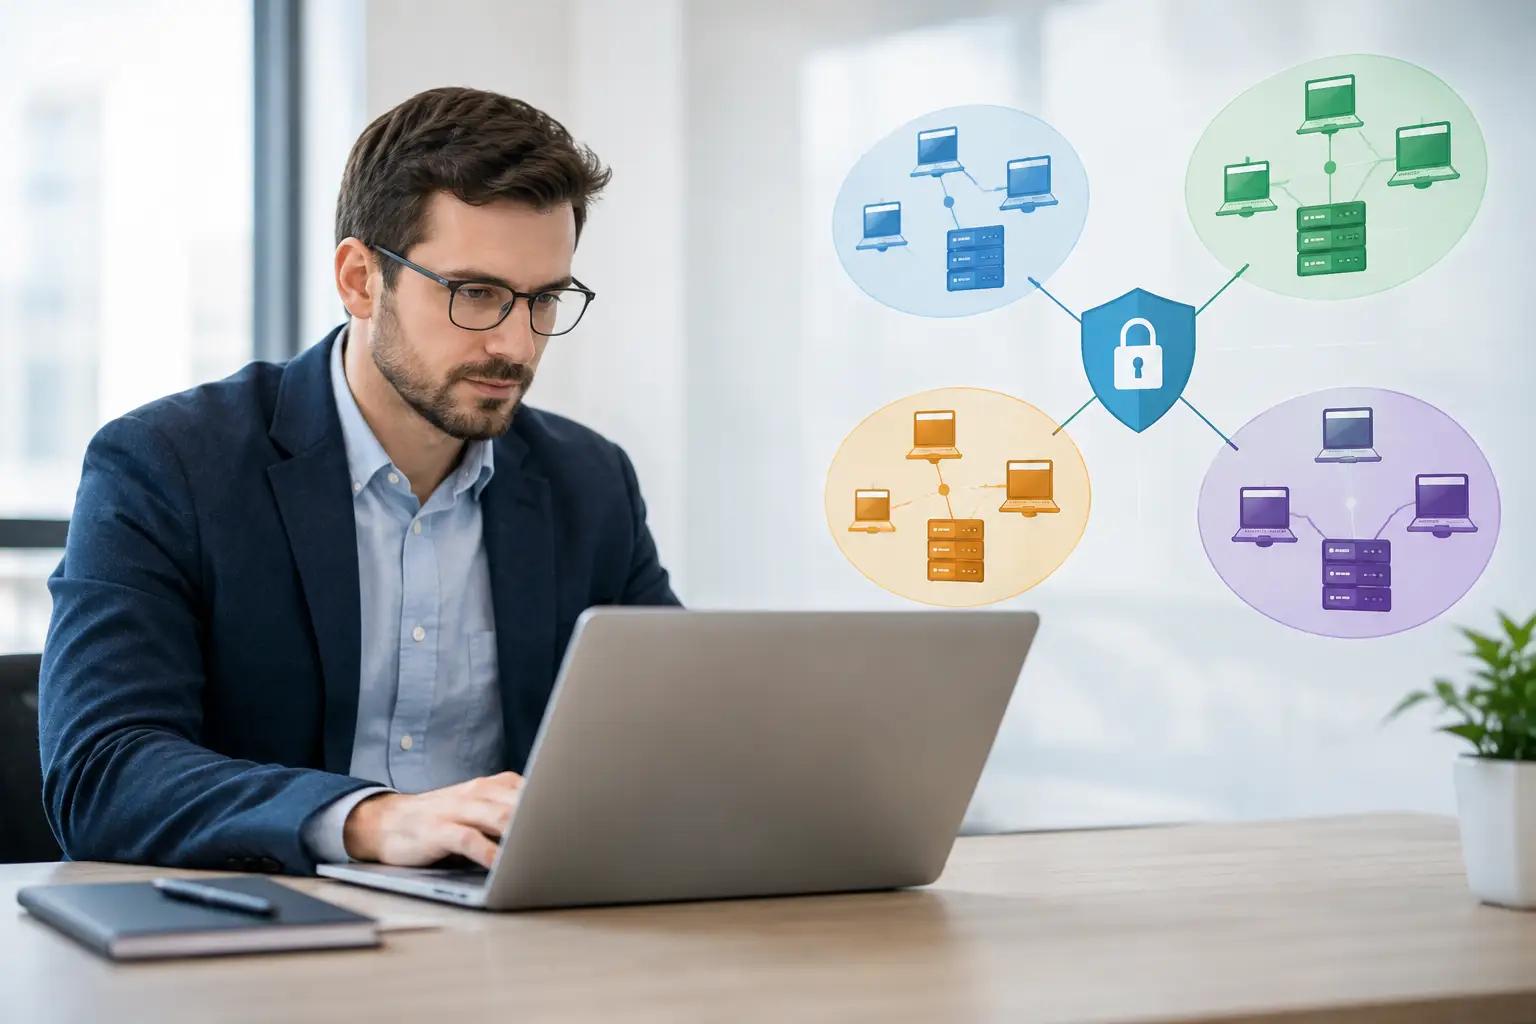
Network segmentation divides an environment into separate zones and controls the traffic permitted between them.
Instead of treating the internal network as a trusted space where most devices can communicate freely, it requires systems to communicate only when there is a defined business reason.
For example, employee laptops may need access to email, approved cloud services, and an application server.
They should not automatically be able to reach backup infrastructure, payment systems, domain controllers, security management consoles, or production databases.
A visitor wireless network should have internet access but no route to internal resources.
Those boundaries can be enforced through firewalls, VLANs, access control lists, identity-based policies, and network access controls.
Benefits of Network Segmentation
| Benefit | Business Impact |
|---|---|
| Reduced Lateral Movement | Limits attacker spread across the environment. |
| Improved Visibility | Suspicious traffic between zones becomes easier to detect. |
| Data Protection | Helps isolate regulated and sensitive information. |
| Faster Recovery | Limits the number of affected systems during incidents. |
| Cyber Insurance Readiness | Demonstrates stronger internal controls to insurers. |
The main security benefit is reduced lateral movement. If a phishing email compromises one user device, segmentation can prevent that compromise from becoming a company-wide outage.
It also improves visibility because unusual traffic between zones becomes easier to identify and investigate.
Network Segmentation Implementation Guide: Start With Risk
The most common mistake is beginning with technology rather than business risk. Buying a firewall or creating VLANs before understanding the systems, users, and data involved often produces a complicated network with weak exceptions and little measurable protection.
Start by identifying the assets that would create the greatest operational, legal, or financial consequences if they were unavailable or exposed. This usually includes customer and employee data, financial records, production applications, identity services, backups, security tools, operational technology, and cloud administration accounts. Map where each asset resides, who uses it, and which applications or services it must communicate with.
Identify business-critical systems before designing segmentation rules. Security controls should be built around business risk, not around network hardware alone.
Example Trust Zones
Then classify systems into practical trust zones.
The exact model depends on the organization, but many businesses need separate zones for user devices, servers, privileged administration, backups, guest and wireless access, third-party connections, cloud workloads, and payment or regulated data.
| Zone | Typical Purpose |
|---|---|
| User Devices | Laptops, workstations, and employee endpoints. |
| Server Zone | Business applications and backend services. |
| Administrative Zone | Privileged accounts and management systems. |
| Backup Zone | Backup repositories and recovery platforms. |
| Guest Network | Internet-only access for visitors. |
| Third-Party Access | Controlled vendor and partner connectivity. |
| Cloud Workloads | Hosted applications and cloud resources. |
| Payment / Regulated Data | Sensitive records requiring additional protection. |
A manufacturing company may also need separate zones for corporate IT and plant-floor systems.
A professional services firm may prioritize client data repositories and remote access infrastructure.
Do not assume that a small business needs a small design.
A 40-person company with sensitive client records and remote staff may have a greater need for clear boundaries than a larger organization with fewer critical systems.
The scope should reflect exposure, not headcount alone.
Define Allowed Traffic Before Blocking It
Segmentation succeeds when policies are based on known, necessary communications. For every connection between zones, document the source, destination, service, port, protocol, business owner, and reason it is required. This creates an access matrix that can be reviewed by IT, operations, compliance, and system owners.
The target state is least privilege: deny traffic by default and permit only what is needed. However, moving to deny-by-default too quickly can stop payroll processing, warehouse operations, customer portals, or backup jobs. A staged approach is safer. Use traffic monitoring to learn existing dependencies, validate them with application owners, then enforce controls in phases.
Access Matrix Example
| Source Zone | Destination Zone | Business Justification |
|---|---|---|
| Employee Workstations | Application Servers | Business application access. |
| Backup Systems | Production Servers | Backup and restoration operations. |
| Vendor Access | Specific Support Platform | Contracted maintenance activities. |
Temporary rules deserve particular attention. A broad exception created to solve an urgent issue can remain in place for years and quietly defeat the design.
Every exception should have an owner, business justification, approval date, and review deadline.
Where possible, use narrowly defined rules instead of allowing an entire subnet to communicate with another subnet.
Build the Architecture Around Critical Boundaries
Technical controls should match the risk of the zone being protected. VLANs can logically separate devices, but they are not enough on their own if routing between VLANs is wide open. Firewalls or layer 3 controls must inspect and restrict traffic moving between zones. For higher-risk environments, internal segmentation firewalls provide more detailed inspection and logging around critical server, data, and administration networks.
Many organizations mistakenly believe VLANs alone provide adequate security. Effective segmentation requires both separation and enforcement. Without traffic controls between segments, attackers can often move freely despite logical network separation.
Protect High-Value Infrastructure First
Protect identity infrastructure and backups as priority zones.
Attackers commonly target domain controllers, privileged access systems, and backup repositories because control over those assets can turn a limited intrusion into a major ransomware event.
Administrative workstations should be separate from standard employee endpoints, and privileged accounts should not be used for routine email, browsing, or document work.
| Critical Asset | Why It Requires Isolation |
|---|---|
| Domain Controllers | Compromise may provide control over the entire environment. |
| Backup Systems | Critical for business recovery after ransomware incidents. |
| Privileged Access Systems | Administrative compromise can significantly increase attacker capabilities. |
| Security Management Consoles | Unauthorized access may disable protection mechanisms. |
| Production Databases | Contain sensitive business and customer information. |
Secure Remote Access and Third-Party Connectivity
Remote access and third-party connectivity also require deliberate boundaries.
Vendors often need access to a specific application or support system, not broad network visibility.
Use authenticated, time-limited access where feasible, restrict the reachable destination, and log activity.
For cloud environments, apply the same principle through separate accounts, virtual networks, security groups, identity roles, and tightly controlled management interfaces.
Grant vendors access only to the systems required to perform their work. Temporary access with automatic expiration significantly reduces long-term exposure.
Test in Stages and Plan for Operations
A segmentation project should be introduced in manageable stages, beginning with a pilot group or one critical boundary. Monitor blocked traffic, application performance, help desk requests, and security logs. When unexpected dependencies appear, determine whether they are legitimate, outdated, or potentially suspicious before adding a new rule.
Testing should include normal business processes and failure scenarios. Confirm that users can complete their jobs, scheduled tasks run correctly, and incident responders can still access required logs and tools. Test backup restoration from a separate zone. During a ransomware incident, backups that are reachable from compromised production systems may be encrypted or deleted along with everything else.
Segmentation Testing Checklist
| Validation Area | Expected Outcome |
|---|---|
| Business Applications | Users can continue normal operations. |
| Security Monitoring | Security tools continue receiving logs. |
| Backup Operations | Backup and restore processes function correctly. |
| Remote Access | Authorized access remains available. |
| Incident Response | Responders retain access to required tools. |
Operational Ownership Matters
Operational ownership matters as much as technical configuration.
Someone must be responsible for approving new connectivity, reviewing firewall rules, removing unused access, and responding to alerts.
Changes in applications, office locations, acquisitions, cloud services, and vendors can all create new paths across the network.
Segmentation is a control that requires ongoing maintenance, not a one-time installation.
Connect Segmentation to Compliance and Cyber Insurance
Many compliance frameworks and customer security questionnaires expect organizations to limit access to sensitive data and separate critical systems from general user networks. Segmentation helps support those requirements, but it is not a substitute for broader controls such as multifactor authentication, endpoint detection and response, patch management, secure backups, incident response planning, and employee awareness training.
It also has practical implications for cyber insurance. Insurers increasingly assess whether an organization can prevent or contain ransomware, protect privileged access, and restore systems after an event. They may ask about network controls, remote access, backup isolation, logging, and endpoint protection during underwriting. Clear documentation of network zones, access rules, reviews, and testing can support more accurate conversations about risk controls.
Cyber Insurance and Network Segmentation
| Insurance Question | How Segmentation Helps |
|---|---|
| Can ransomware be contained? | Limits lateral movement across systems. |
| Are privileged systems protected? | Creates separate administration zones. |
| Can backups be isolated? | Separates recovery infrastructure from production systems. |
| Is critical data protected? | Restricts access to sensitive assets. |
Coverage should be reviewed alongside the technical program. Even strong segmentation cannot eliminate business interruption, notification expenses, legal costs, digital forensics, extortion demands, or third-party liability after a serious incident. Conversely, insurance cannot restore a poorly protected environment quickly. The strongest position combines prevention, containment, documented recovery capability, appropriate coverage, and support when a claim occurs.
Measure Whether Segmentation Is Working
A useful program has evidence, not just diagrams. Review the number of unrestricted paths to critical assets, the percentage of firewall rules with a documented owner and purpose, privileged access routes, blocked connection attempts, and the time required to isolate an affected endpoint. Track exceptions as a risk register, especially rules that permit broad access between user and server networks.
| Metric | Why It Matters |
|---|---|
| Open Paths to Critical Assets | Measures attack surface exposure. |
| Documented Firewall Rules | Improves governance and control ownership. |
| Blocked Connection Attempts | Indicates effectiveness of segmentation controls. |
| Isolation Response Time | Measures operational readiness during incidents. |
Periodic access reviews are essential. A rule that was justified for a project six months ago may no longer be necessary. Vulnerability scanning and penetration testing can also identify unexpected routes between segments. If a test user on a standard workstation can reach backup administration or a sensitive database without a legitimate business requirement, the boundary requires immediate attention.
Network segmentation is most valuable before an incident reveals the weaknesses in an organization’s architecture. Businesses that prioritize critical boundaries, maintain clear access controls, regularly test recovery procedures, and combine segmentation with broader security controls are significantly better positioned to withstand ransomware, reduce cyber insurance risk, and recover more efficiently after an attack.
Frequently Asked Questions
What is network segmentation?
Network segmentation is the practice of dividing a network into separate security zones and controlling communications between them to reduce cyber risk and limit attacker movement.
Why is network segmentation important for ransomware protection?
Segmentation helps prevent lateral movement by restricting attackers from spreading from a compromised workstation to servers, backups, databases, and other critical business systems.
Which systems should be placed in separate network segments?
Organizations typically separate user endpoints, servers, backup systems, privileged administration systems, guest networks, cloud workloads, databases, and regulated data environments.
What does a “deny by default” approach mean?
A deny-by-default model blocks all traffic between network segments unless there is a documented business requirement that specifically permits the communication.
What technologies are commonly used for network segmentation?
Network segmentation is commonly implemented using VLANs, firewalls, access control lists (ACLs), network access control (NAC) solutions, Zero Trust architectures, and identity-based security policies.
Written by Maria Veleva
Managing Partner @ BALKAN INSURANCE BROKERS | Published on
With over 20 years in insurance mediation and an EMBA in Finance, Maria advises businesses on property and casualty insurance, risk strategy, and corporate finance across SE Europe.